01
API and integration architecture
Define system boundaries, contracts, identities, ownership and the right combination of synchronous APIs and asynchronous messages.
- REST and webhook contracts
- Middleware and adapters
- Versioning and compatibility
 KEEN SYSTEMSGet a Quote
Connect ERP, finance, ecommerce, booking, support, mobile and partner platforms through clear contracts, validated data flows, resilient messaging and operational visibility.

Integration is not simply transferring fields. It requires ownership, identity, mapping, timing, validation, permissions, failure handling, reconciliation and support. A professional integration makes these decisions explicit so connected platforms remain dependable as vendors and workflows evolve.
Twelve views of the workflows, boundaries and technology contexts that dependable integrations must connect.
12Integration and platform views
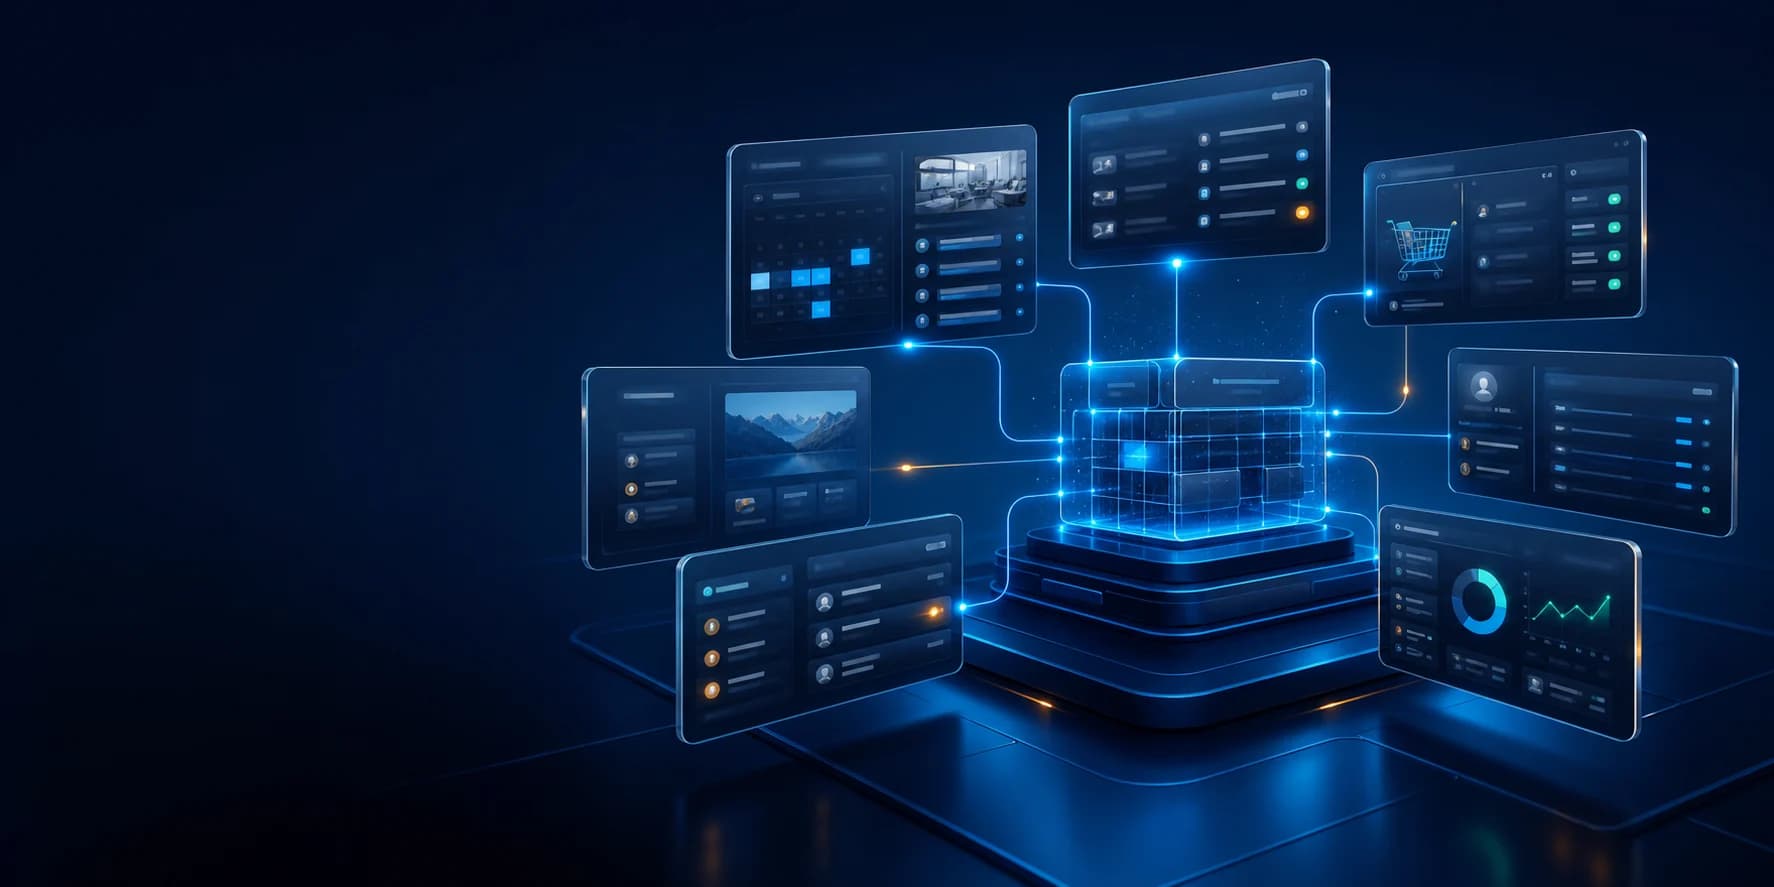
Integration layers that connect business functions without hiding ownership or system boundaries.
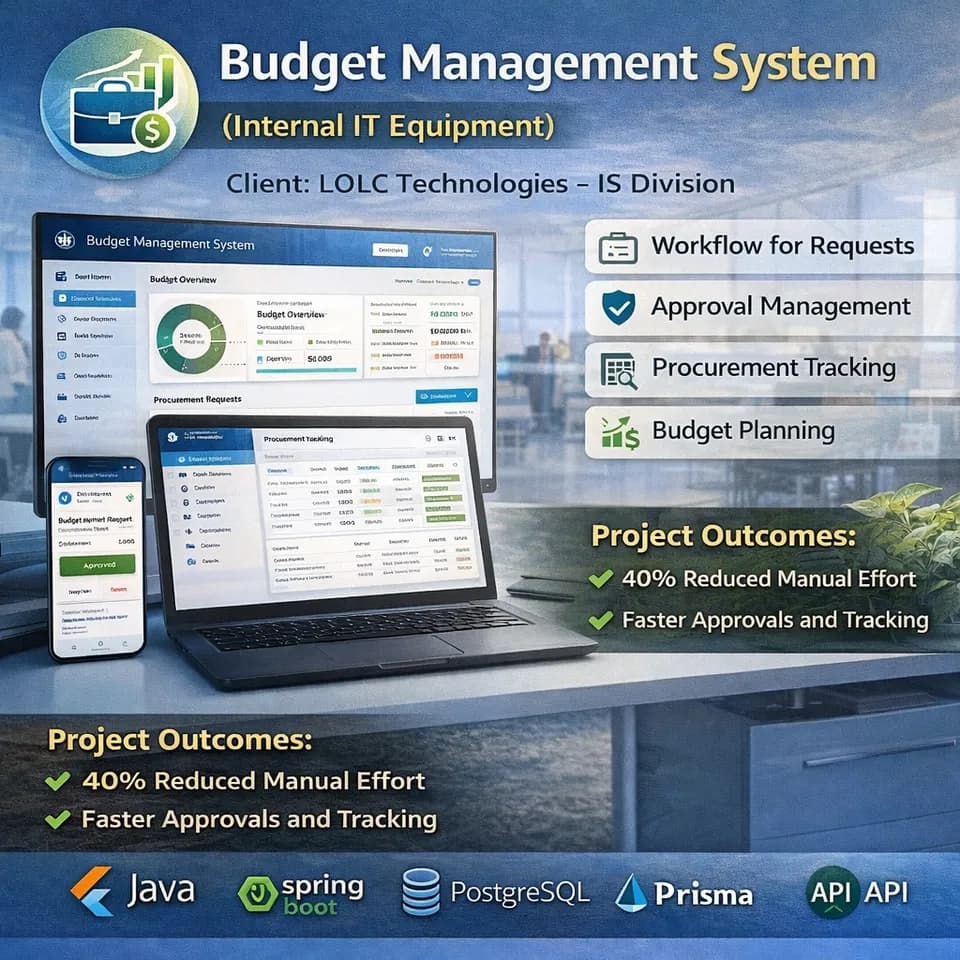
Requests, approvals and financial records joined through controlled service contracts.
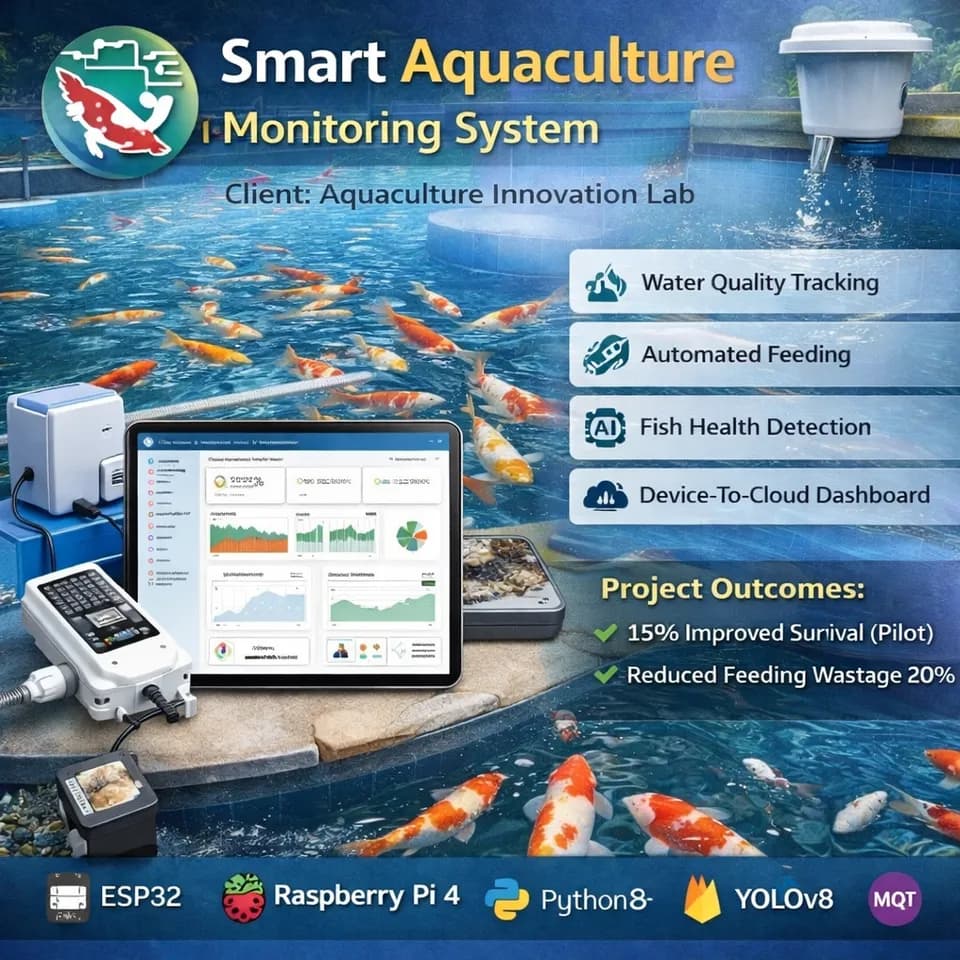
Validated device data routed into dashboards, alerts and operational decisions.
Customer, schedule and service information coordinated across role-aware interfaces.
Reliable hand-offs between discovery, enquiry, booking and administration systems.
Forecasts, inventory signals and alerts delivered from shared data services to field users.
Cloud foundations for secure exchange, controlled scaling and resilient integration workloads.
Scoped credentials, permissions and secure transport across every connected boundary.
Traceable exchanges linking equipment, sensors, applications and operational reporting.
Well-defined data contracts that support analytics, automation and machine-learning services.
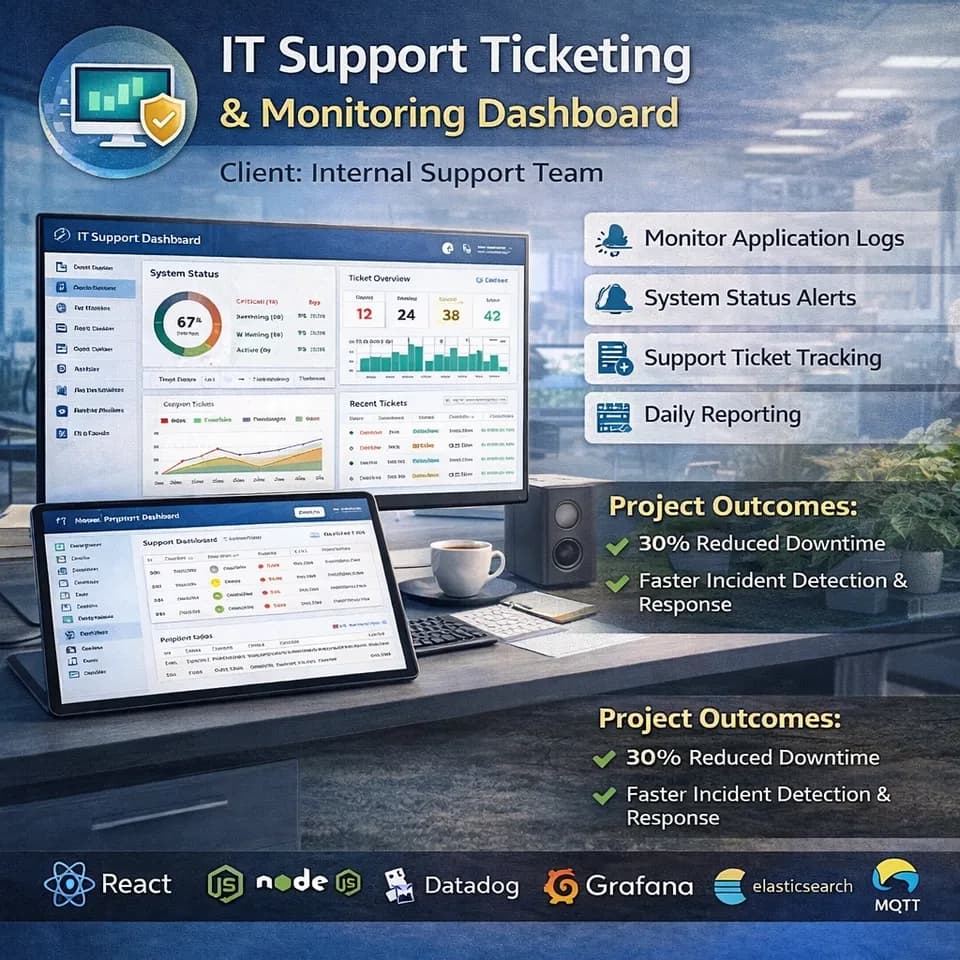
Operational views that expose health, incidents, queues and the boundary needing attention.
Stable interfaces that support mobile, web and partner experiences from shared capabilities.
The final engagement can combine these areas or begin with a focused assessment and prioritised first stage.
Define system boundaries, contracts, identities, ownership and the right combination of synchronous APIs and asynchronous messages.
Translate records and events between platforms while preserving validation, transaction meaning and exception handling.
Protect credentials and data, trace exchanges, manage retries and provide operators with useful status and diagnostics.
Technology is evaluated against integration, maintainability, security, performance, data and support needs. A fashionable tool is not automatically the right operational choice.
Interface style is selected around latency, ownership, change control, data volume and the capabilities exposed by each connected platform.
Dedicated services isolate vendor details, apply mapping and validation, coordinate workflow and keep business systems from depending directly on unstable external formats.
Persistent integration state and messaging patterns support retries, deduplication, traceability and controlled asynchronous work.
Operational controls help teams answer what moved, what failed, whether retry is safe and which system owns the correction.
Review points keep scope, architecture, operational readiness and evidence visible throughout delivery.
Clarify the business outcome, users, current systems, constraints, risks, ownership and evidence required to call the work successful.
Turn the discovery findings into boundaries, modules, interfaces, milestones, quality expectations and an implementation path.
Build and validate working increments so stakeholders can examine behaviour, data, usability and operational readiness before release.
Prepare environments, monitoring, documentation, access, rollback expectations and support ownership before production use begins.
Use production evidence, user feedback and service indicators to prioritise improvements without losing architectural discipline.
A detailed, answer-ready guide for business owners, product teams, technical leaders and operators evaluating this service.
Direct answer: Before integration, teams should decide which system owns each business fact, which events trigger exchange, which rules apply, who resolves exceptions and how correctness will be verified.
A reliable integration begins with business ownership because technical connectivity cannot resolve conflicting definitions.
Map entities, identifiers, lifecycle, authorities, timing, reference data, approval points and the consequences of each system being unavailable.
Document source-of-truth decisions, event vocabulary, responsibility boundaries and example transactions before finalising API or message design.
Risks include both systems editing the same fact, circular synchronisation, ambiguous identifiers, undocumented manual corrections and ownership that changes depending on the report.
Evidence includes consistent ownership answers, fewer reconciliation disputes, traceable state transitions and exception queues routed to an accountable team.
Direct answer: A dependable API has clear resources or commands, stable meaning, validated inputs, explicit errors, appropriate authentication, versioning expectations, idempotency where required and documentation with realistic examples.
An API is a long-lived agreement between teams and systems, not merely a route that returns data.
Clarify consumers, latency, volume, consistency, compatibility, pagination, filtering, rate limits, permissions, error semantics and support ownership.
Use contract-first examples where useful, validate at the boundary, keep errors actionable, separate internal models and test consumer-important behaviour.
Risks include exposing database structures, breaking optional fields, inconsistent status codes, unbounded responses, weak authentication and consumers depending on undocumented behaviour.
Track contract changes, consumer failures, latency, error distribution, deprecated usage, documentation gaps and the time needed to diagnose a rejected request.
Direct answer: Data mapping should translate meaning, identity, format, units, status and required relationships explicitly, with validation and exception handling for records that cannot be converted safely.
Fields with similar labels may represent different rules, while one business concept may be split across several records in another platform.
Compare schemas, samples, nullability, enumerations, codes, timezones, currencies, precision, lifecycle and the ownership of shared reference data.
Maintain versioned mapping rules, validation reports, reference lookups, transformation tests and a quarantine path for unsafe records.
Risks include silent defaulting, loss of precision, timezone drift, unknown codes, partial relationships, truncation and mappings maintained only in an individual's spreadsheet.
Use acceptance rate, exception categories, manual corrections, reference-data mismatches, reconciliation totals and repeat failure after correction.
Direct answer: Events and queues are useful when work can happen asynchronously, traffic needs buffering, producers and consumers should be decoupled, or reliable retry is more important than an immediate response.
Asynchronous design changes how completion, failure, ordering and user feedback must be understood.
Define event meaning, delivery guarantees, ordering needs, retry policy, dead-letter handling, idempotency, retention, schema evolution and operator visibility.
Publish stable business events, include trace context, make consumers safely repeatable, monitor backlog and provide controlled replay or correction paths.
Risks include duplicate effects, poison messages, hidden backlog, uncontrolled replay, assumptions of global order and events that expose internal implementation rather than business meaning.
Track queue age, throughput, retry distribution, dead letters, duplicate suppression, processing latency and time to resolve a stuck business transaction.
Direct answer: ERP and financial integration must preserve transaction identity, amounts, tax meaning, posting state, reference data, approvals and reconciliation, with correction paths that respect accounting and operational controls.
Transactional integrations carry consequences beyond screen consistency because downstream records may affect stock, cash, liabilities or reporting.
Define posting boundaries, document numbers, currency and rounding, tax codes, branch and warehouse context, cancellation, reversal, partial completion and cut-off timing.
Use idempotent transaction keys, validation before posting, immutable references where appropriate, explicit reversal flows and reconciliation reports agreed with business owners.
Risks include duplicate posting, silent amount differences, out-of-order cancellation, stale master data, partial stock movement and corrections made outside the documented process.
Review balanced totals, unmatched references, duplicate prevention, posting latency, correction volume, period-end reconciliation effort and audit trace completeness.
Direct answer: Integration access should use dedicated identities, least-privilege permissions, protected credentials, clear rotation and revocation, secure transport and logs that identify the acting system without exposing secrets.
Machine identities often have broad unattended access, making their lifecycle and scope as important as human accounts.
Identify trust boundaries, credential owner, token lifetime, scopes, network exposure, data classification, rotation process, emergency revocation and vendor limitations.
Store secrets outside source code, use scoped service accounts, validate tokens, restrict network paths where useful and separate test from production identities.
Risks include shared permanent credentials, production secrets in test tools, overly broad scopes, credentials in logs, unowned certificates and integration access that survives contract termination.
Track credential age, scope reviews, failed authentication, rotation success, inactive identities, access exceptions and whether every integration identity has an owner.
Direct answer: Resilience comes from isolating vendor behaviour behind adapters, controlling timeouts and retries, validating assumptions, buffering where appropriate, monitoring dependency health and planning for contract change.
Connected systems may be slow, rate-limited, inconsistently documented or changed outside the integration team's control.
Record supported interfaces, vendor limits, maintenance windows, known failure modes, support channels, sandbox differences, change notice and alternatives for critical workflows.
Use anti-corruption adapters, defensive parsing, bounded retries, circuit breakers where suitable, cached reference data and feature controls for uncertain dependencies.
Risks include endless retries, cascading resource exhaustion, vendor data accepted without validation, production-only behaviour, screen scraping and hidden dependence on deprecated endpoints.
Track dependency latency, availability, throttling, timeout rate, fallback use, vendor incidents, contract changes and user impact attributable to the dependency.
Direct answer: Integration testing should validate contracts, transformations, permissions, retries, duplicates, ordering, partial failure and business reconciliation using representative data and controlled environments.
A successful HTTP response does not prove that the intended business outcome occurred correctly in every connected system.
Identify critical transaction examples, edge cases, volume, invalid inputs, duplicate delivery, unavailable dependencies, correction workflows and the totals or states that should reconcile.
Combine unit tests for mapping, contract tests, sandbox integration, controlled end-to-end scenarios and post-run reconciliation with trace identifiers.
Risks include idealised test data, shared unstable sandboxes, destructive tests, missing negative cases, no verification in the destination and manual testing that cannot be repeated.
Use contract pass rate, mapping defects, reconciliation variance, test reliability, production escape, correction effort and time required to locate the failing boundary.
Direct answer: Production integrations need ownership, health and business-flow monitoring, traceability, actionable alerts, retry and correction procedures, change governance and regular review of contracts and credentials.
Integration failures often sit between team boundaries, so support needs a shared view of evidence and responsibility.
Define service owners, escalation, dashboards, alert actions, business reconciliation, support hours, vendor contacts, replay authority, maintenance and deprecation policy.
Provide correlation search, transaction status, queue health, dependency indicators, runbooks, controlled replay tools and versioned interface documentation.
Risks include technical health without business completion, alerts sent to nobody, unsafe manual replay, undocumented vendor changes and failed records accumulating outside an owned queue.
Review completion rate, backlog age, mean diagnosis, replay success, unresolved exceptions, contract currency, alert quality and stakeholder confidence in reconciliation.
Real projects that demonstrate relevant workflow or technology experience.
A workflow platform supporting requests, approvals, procurement tracking and budget planning through REST-based services.
A connected booking and support module handling schedules, patient records, cancellation and operational access.
Concise answers to common planning, scope and operating questions.
Often, yes. The approach depends on the ERP's supported APIs, data model, permissions, vendor policy and transaction rules. Discovery should confirm safe integration boundaries before implementation.
Options may include supported file exchange, database views approved by the owner, vendor-provided connectors or a process change. Screen scraping is fragile and should be treated cautiously.
Yes, when the connected systems and business need support it. Real-time may use APIs, webhooks or events. Some workflows are safer and more economical as controlled batches.
The design can use bounded retries, idempotency, dead-letter or exception queues, operator visibility and controlled correction or replay according to the transaction risk.
Stable identifiers, idempotency keys, ownership rules, deduplication checks and reconciliation are common controls. The exact combination depends on the transaction and systems.
Yes. Integration commonly exists to preserve valuable systems while creating a controlled information flow or new user experience around them.

Bespoke web, mobile and internal platforms designed around the way your organisation operates.
View service
ERP, IoT, AI, automation and custom hardware integrated solutions.
View service
Cloud foundations, automated delivery pipelines, containers, observability and production controls.
View service
Monitoring, incident response, updates, performance work and continuous care for production applications.
View service
Distinctive business websites with responsive design, useful content and search foundations.
View service
Customer portals, operational dashboards and business workflows built around your team.
View serviceShare the system context, users, current constraints and outcome you want to improve. The first conversation can focus on the most useful next step.